What original means here
Mega888 is a platform supplier rather than a casino you sign up with directly. One app holds the slots, fishing, arcade and table games, and the account you use inside it comes from an agent or from a casino that offers the platform in its lobby. That structure is why so many different sites end up hosting the installer: the file travels further than the company that built it.
So a Mega888 original download is not a question of which site looks more convincing. It is a question of whether the bytes you received match the bytes that were published. Three outcomes are possible when you grab an installer from a reposted link. It is the same file, which is fine. It is an older build, which may still install but can stop logging in later. Or it has been modified and re-signed, which is the case to catch.
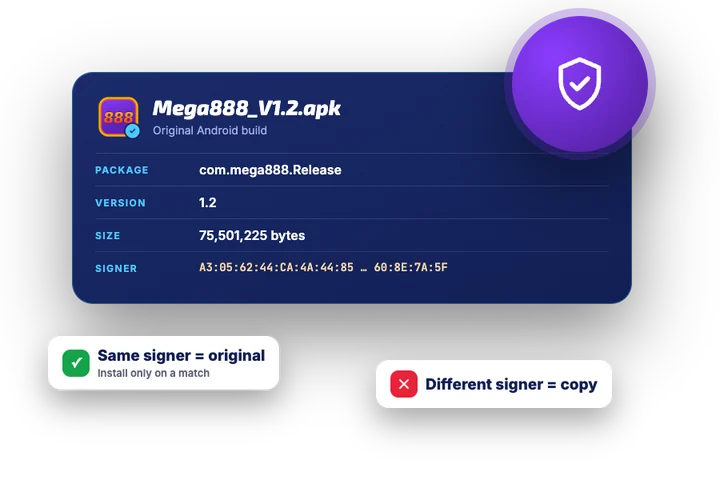
The good news is that a Mega888 original APK can be identified without guessing, using values that are fixed for build 1.2.
Inside the original Mega888 APK
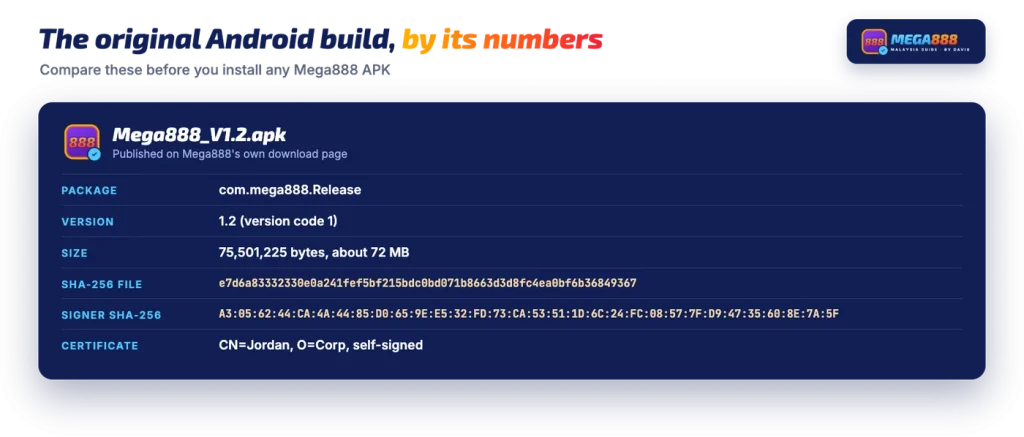
These are the identifiers of the published Android build. Record them somewhere before you start, then compare.
| Detail | Mega888 build 1.2, Android |
|---|---|
| Package name | com.mega888.Release |
| Version | 1.2, version code 1 |
| File size | 75,501,225 bytes, about 72 MB |
| SHA-256 of the APK file | e7d6a83332330e0a241fef5bf215bdc0bd071b8663d3d8fc4ea0bf6b36849367 |
| Signing certificate SHA-256 fingerprint | A3:05:62:44:CA:4A:44:85:D0:65:9E:E5:32:FD:73:CA:53:51:1D:6C:24:FC:08:57:7F:D9:47:35:60:8E:7A:5F |
| Certificate holder | CN=Jordan, O=Corp, self-signed |
| Certificate valid from | 24 April |
| Android support | minSdkVersion 19, Android 4.4 and newer, targeting API 29 |
The targeting value matters for newer phones. As a rule, Android 14 and later refuse to install apps that target below API level 23, and this build targets 29, so the current file is not affected by that block. The permission prompts and Play Protect wording are covered in installing the APK on Android.
Checking the file before you install
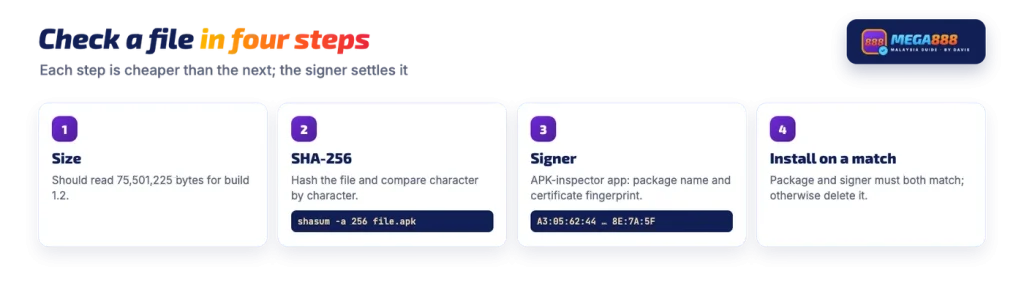
Work through the checks in order, because each one is cheaper than the next and the early ones catch the obvious cases.
- Compare the size. Your file manager shows the exact byte count in the file details. For build 1.2 it should read 75,501,225 bytes. A file that is a few megabytes off is a different build; a file that is dramatically smaller can be a downloader wrapper rather than the app.
- Compute the SHA-256 of the file. On Android, a file-hash app does it in a few taps. On a computer, use sha256sum on Linux, shasum -a 256 on macOS, or certutil -hashfile in Windows Command Prompt. Compare the result character by character with the hash in the sheet above.
- Read the package name and signer. Open the APK in an APK-inspector app. It will show the declared package name, the version, and the SHA-256 fingerprint of the signing certificate. Both the package name and the fingerprint must match exactly.
- Install only on a match. If the package name and the signing fingerprint both line up, continue with installing the APK on Android in the normal way. If either one differs, delete the file and get the installer from the agent or casino that issued your account.
A mismatch is not always sinister. A hash that does not match while the package name and signer do points to a different version number, a separate question covered under when a new build appears.
Why the signer matters more than the hash
A file hash is a fingerprint of one exact file. Change a single byte and the hash changes completely, which is what makes it precise and also what makes it fragile: every new release produces a new hash, and a hash you copied from somewhere may simply be out of date.
The signing certificate behaves differently. In general on Android, the developer signs each release with the same private key, and Android itself refuses to update an installed app with a build signed by a different key. Nobody can take the original installer, modify it, and keep the original signature. They have to re-sign with their own key, and the fingerprint changes. That is the check that survives version changes.
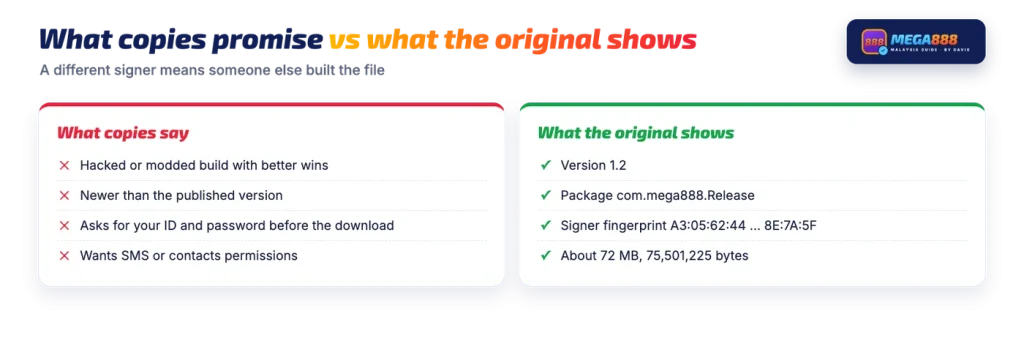
What copies say
A newer, faster or hacked build with better wins, modded credits or an unlocked version.
What the original shows
Version 1.2, package name com.mega888.Release, and a signing fingerprint that begins A3:05:62:44 and ends 8E:7A:5F. In general, nothing inside an installer decides game results; on platforms like this the outcome is decided on the server the app connects to.
The original Mega888 app on iPhone
There is no APK on iOS, so the Android checks do not transfer. A single Mega888 original download iOS APK file does not exist: the APK is Android only, and iPhones install a separate iOS build of the same version.
That build carries the bundle identifier com.mega888.Release and bundle version 1.2, matching the Android package name. It does not come from the App Store. Instead it installs through Apple’s enterprise distribution route, which means Safari opens an install prompt and the icon then appears on the home screen.
On iPhone, the trust step is the check. On iOS, the first launch of an app installed this way reports an untrusted enterprise developer until you approve the profile under Settings > General > VPN & Device Management. Look at that screen before approving, because trusting a profile applies to everything that profile signed, not just one app. If you did not get the install link from the source that issued your account, that is the moment to stop. Apple can also revoke an enterprise certificate at any time, and in general an app installed that way stops opening until a re-signed build is installed.
Signs of a copy
- A declared package name that is anything other than com.mega888.Release.
- An installer labelled 1.2 that is far smaller or larger than about 72 MB.
- Requests during install for permissions the app has no use for, such as SMS or contacts, which in general is a sign of a repackaged build.
- A page that wants your user ID and password before it will hand over the file. Nothing about downloading an installer requires your login.
- A build advertised as modded, cracked, hacked or patched for higher wins.
- An installer renamed to look current while the version inside still reads lower than the published build.
Hashing files and reading signing certificates is a fair amount of work for one app. Some Malaysian online casinos run Mega888 inside their own lobby instead, so there is no installer to sideload and the balance sits in the casino wallet.
If you already installed a copy
Uninstall it first, so the repackaged build is no longer running on the phone. Then change your password through whoever issued the account, since in general a modified client is in a position to see whatever you typed into it. Only after that should you install the published build, taken from the agent or casino that gave you the account, and verified against the package name and signer above.
If anything about the account looks wrong after that, raise it with the issuer rather than with any site offering to fix it. The install and account overview sets out what the issuer handles and what the app itself can do. This guide is for adults 21 and over, and gambling carries risk.
FAQ
How do I know my Mega888 APK is original?
Compare three things against the published build 1.2: the file size of 75,501,225 bytes (about 72 MB), the package name com.mega888.Release, and the signing certificate fingerprint beginning A3:05:62:44 and ending 8E:7A:5F. The signer is the strongest of the three, because it stays the same across builds while the file hash changes with every new release.
What is the package name of the Android build?
com.mega888.Release. The version name is 1.2 and the version code is 1. The same identifier is used on iOS as the bundle identifier. An installer that declares any other package name is a different app, whatever its icon or title says.
Is a mod APK safe to install?
A modified build is, by definition, not the file the platform published, and it has been repackaged and re-signed by someone else. No modification can change what a server decides about credits or results, so claims of better wins have nothing behind them. A modded installer also loses the one check that works: the original signing fingerprint.
Does a different file size mean the file is fake?
Not on its own. A different size can simply mean a different build number. For build 1.2 specifically the Android file is 75,501,225 bytes, so a file labelled 1.2 that is far smaller or larger deserves a closer look. Settle the question with the package name and the signing fingerprint rather than the size.
How do I check the original on an iPhone?
There is no APK to inspect on iOS. The iOS build carries the bundle identifier com.mega888.Release and version 1.2, installs through Apple’s enterprise route rather than the App Store, and asks you to trust a developer profile under Settings > General > VPN & Device Management. Install it only from the same source that issued your account, since a profile you trust applies to whatever that profile signed.